Corporate CI/CD pipeline on AWS: from a commit to a scanned, quality-gated release running on Kubernetes.
- Client
- Open source reference
- Key result
- 17 automated stages, security gates at build and image level
- Live
- github.com ↗
Context
Most pipelines stop at build and deploy. A corporate pipeline has to prove, at every release, that the code meets a quality bar and ships no known vulnerability, and that what runs in production is observed.
What I built
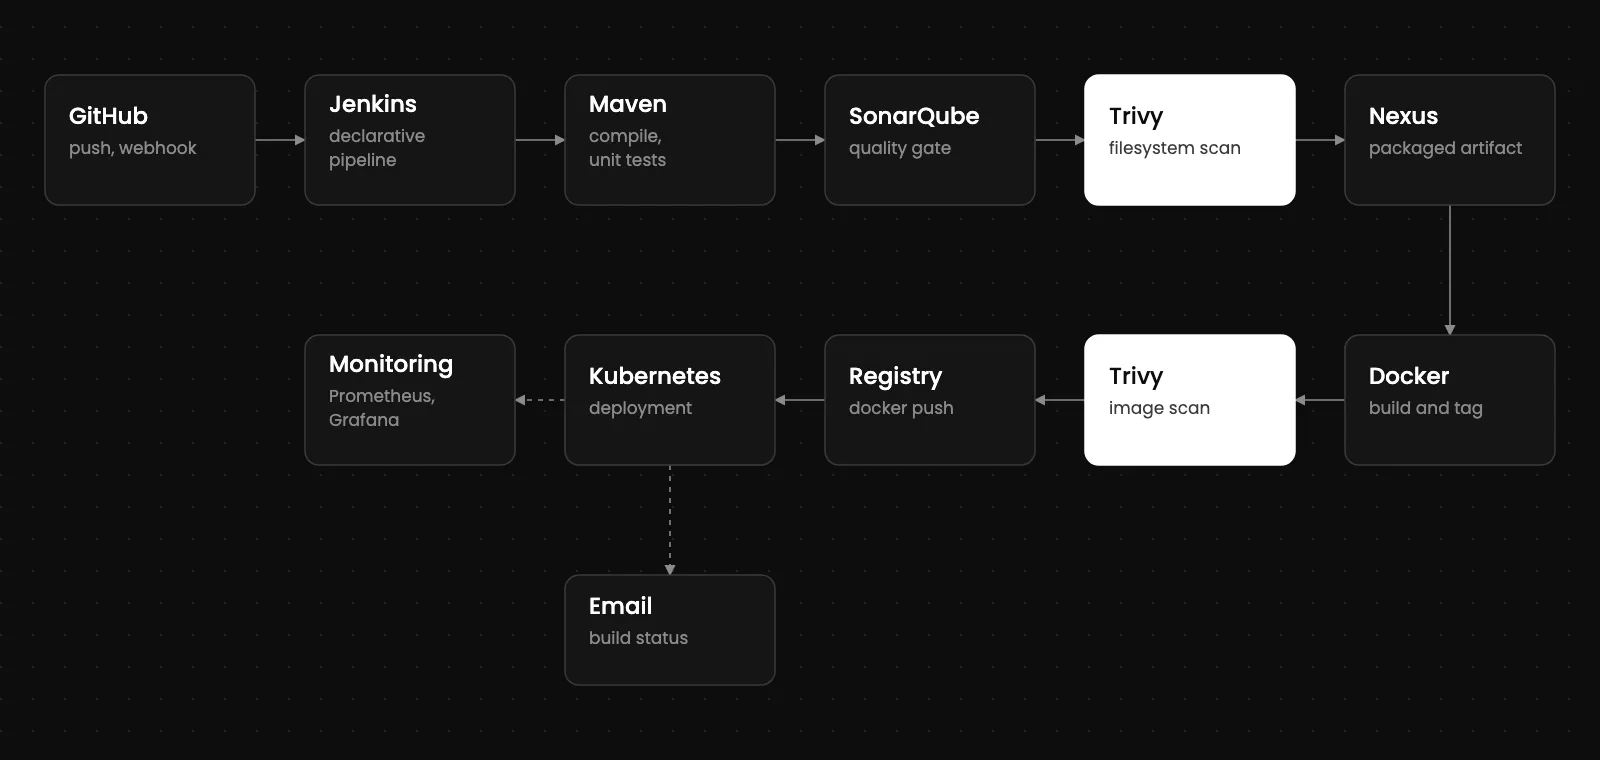
The full infrastructure provisioned on AWS EC2: a Kubernetes cluster, SonarQube, Nexus and Jenkins on dedicated instances. The Jenkins pipeline compiles and tests with Maven, scans the file system with Trivy, runs SonarQube analysis and blocks on its quality gate, publishes versioned artifacts to Nexus, then builds, tags and scans the Docker image before pushing it and deploying to Kubernetes, where it verifies pods and services. Prometheus and Grafana, installed with Helm, monitor both the cluster and the application, and Jenkins reports each run by email.
Result
A reproducible, documented blueprint where nothing reaches the cluster without passing tests, the quality gate and two vulnerability scans. Shared on LinkedIn, where it drew close to 300 reactions.
Stack
- Jenkins
- Kubernetes
- AWS EC2
- SonarQube
- Trivy
- Nexus
- Docker
- Helm
- Prometheus
- Grafana
- Maven