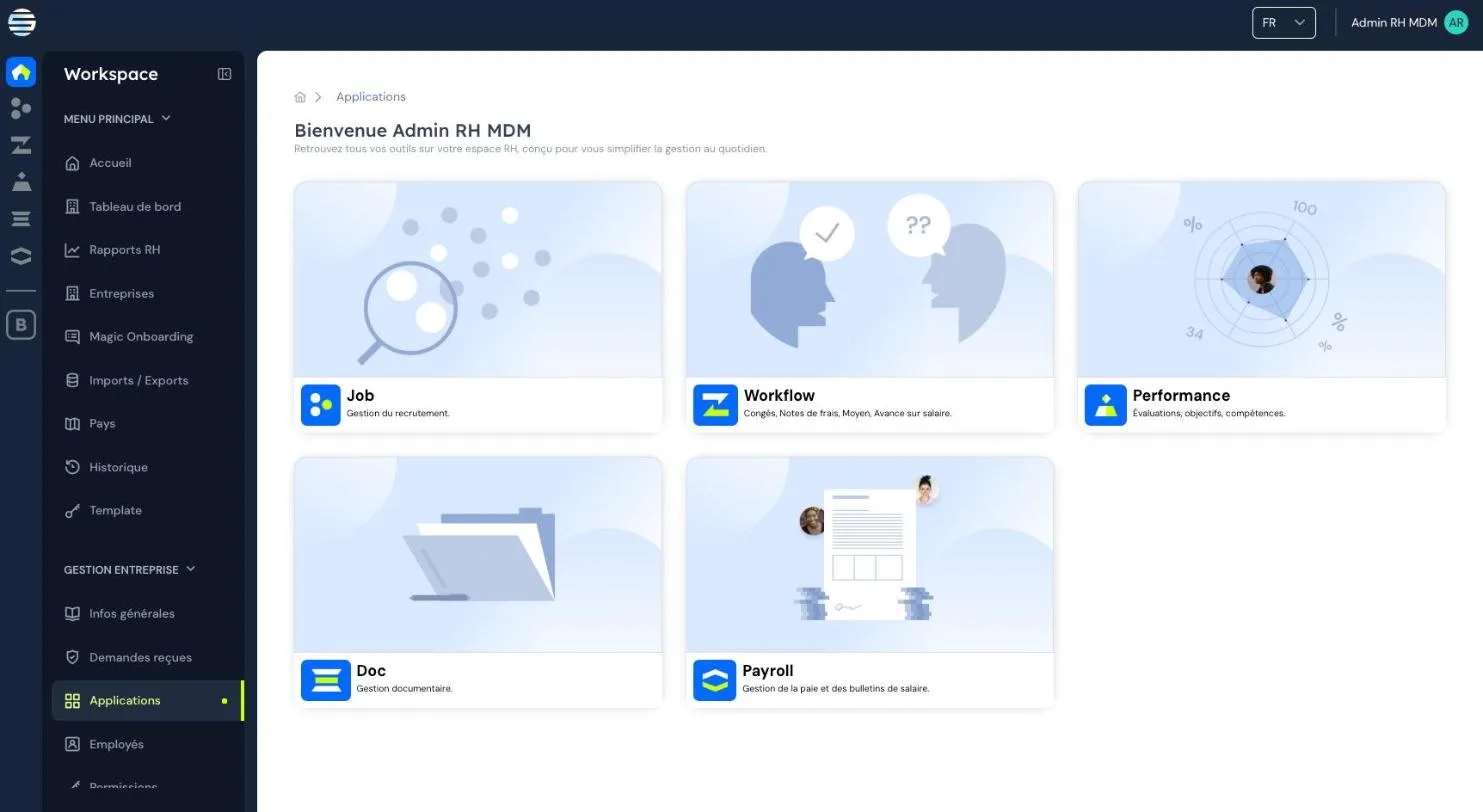
Core HR: employee records, seniority, absences, offboarding and reporting.
- Client
- Socium
- Key result
- HR reports with 143 KPIs
Context
Core HR data feeds every other app of the suite: if seniority, absences or job descriptions are wrong in Workspace, leave rights, evaluations and reports are wrong everywhere.
What I built
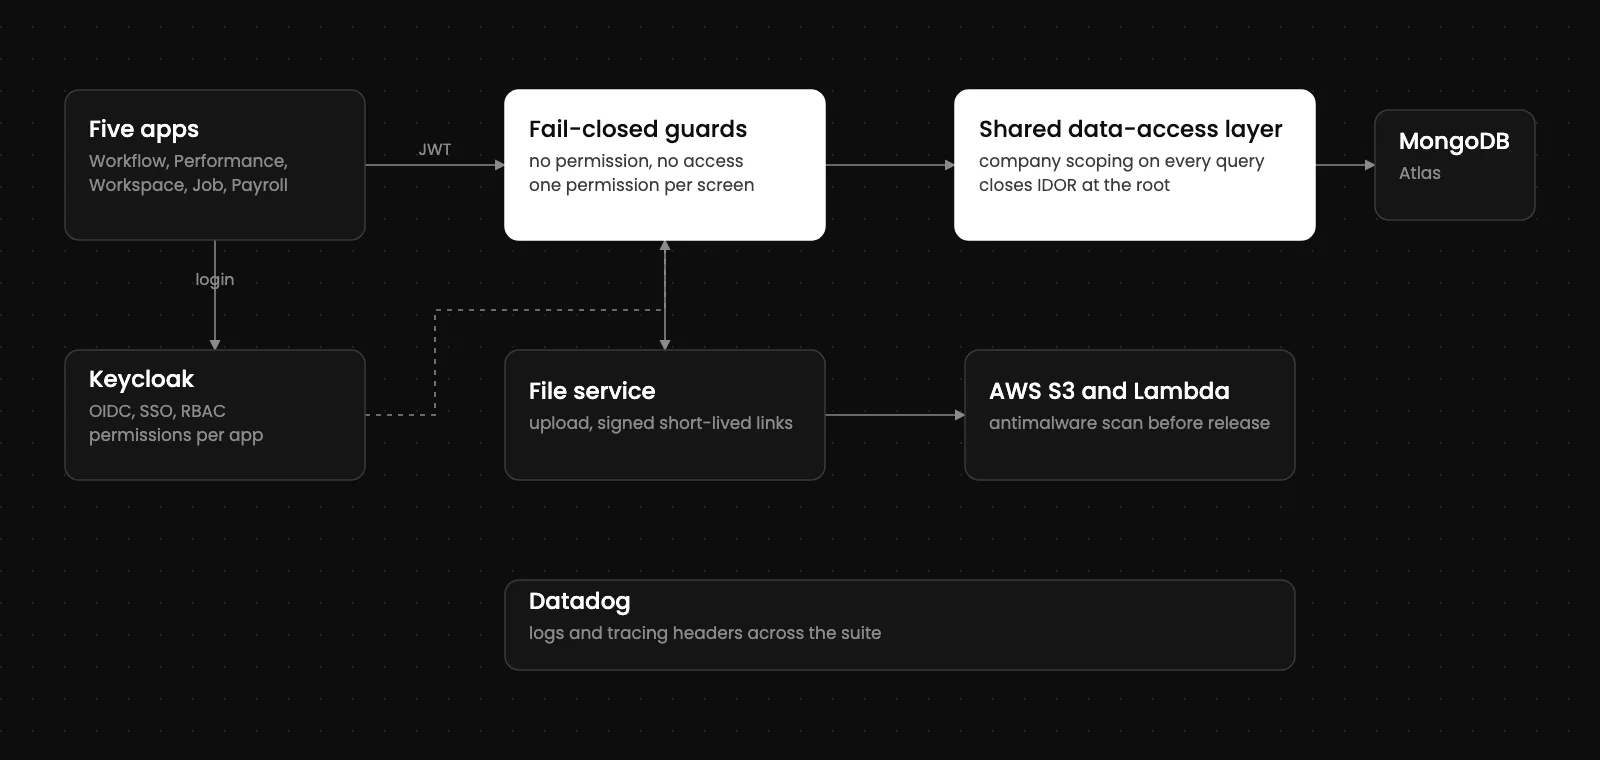
Seniority computed from hiring dates, absences and absence rate, skills and trainings linked to job descriptions, offboarding that deactivates the Keycloak account automatically, and an HR reporting module with 143 KPIs, scheduled delivery and PDF rendering. Security is shared by the whole suite: after a penetration test found tenant isolation and IDOR weaknesses, I moved tenant isolation into a shared data-access layer instead of each endpoint, with fail-closed guards and per-app permissions on Keycloak, a file service on S3 with antimalware scanning and short-lived signed links, and Datadog logging across the five apps.
Result
One security model shared by the five apps, closing the penetration test findings at the root.
Architecture
Seniority computed, not stored
Seniority is derived on the fly from the hiring date, with explicit overrides, so it never drifts from the contract.
Offboarding closes access
Ending a contract deactivates the employee's Keycloak account automatically, instead of relying on someone to remember.
Reports as templates over a KPI catalogue
143 KPIs feed report templates that a serverless job renders as PDF and sends on schedule, with holding and subsidiary comparisons.
Security shared by the whole suite
Tenant isolation lives in the shared data layer and files go through one secure service, so every app gets the same protection.
Stack
- Angular
- NestJS
- MongoDB
- Keycloak
- AWS S3
- AWS Lambda
- Datadog